Table of Contents
Windows Firewall Control: Complete Guide to Windows Firewall, Ports, Rules, and Network Security
Windows Firewall Control is a term commonly used for tools and settings that help users manage Windows Firewall rules, applications, network connections, and open ports. On modern Windows systems, the built-in Microsoft Defender Firewall is already integrated into Windows Security and provides network traffic filtering for Windows 10 and Windows 11. (Microsoft Support)
For users searching for Windows Firewall Control, Windows Firewall Control download, Windows Firewall Control panel, Windows Firewall Control (WFC), or ways to configure ports such as 9999 and 7777, it is important to understand the difference between Windows Firewall itself and third-party management utilities.
Windows Firewall controls which network traffic is allowed to enter or leave a computer. Rules can be created for applications, ports, IP addresses, protocols, and network profiles. Windows also provides advanced firewall management through the Windows Security interface, Control Panel, and Windows Defender Firewall with Advanced Security.
This guide explains how Windows Firewall works, how to check whether it is enabled, how to open and close ports, what TCP port 9999 means, how port 7777 can be opened when required, what happens when the firewall is disabled, and why allowing a specific application is often preferable to turning the entire firewall off.
What Is Windows Firewall Control?
Windows Firewall Control can refer to two related concepts.
First, it can mean controlling the firewall built into Windows through Windows Security and its advanced configuration tools.
Second, Windows Firewall Control (WFC) is also the name associated with a third-party firewall management utility that provides a more convenient interface for managing Windows Firewall rules.
The underlying Microsoft firewall is called Microsoft Defender Firewall. It is built into Windows and filters network traffic according to configured rules. Microsoft states that Windows Firewall can control traffic using criteria such as IP addresses, network ports, and application paths. (Microsoft Support)
Windows provides several ways to manage these settings:
- Windows Security
- Control Panel
- Windows Defender Firewall with Advanced Security
- Command-line tools
- PowerShell
- Third-party firewall-management utilities
The standard Windows Security interface is enough for many everyday users, while Advanced Security provides much more detailed control.
How Does Windows Firewall Work?
A firewall acts as a filtering layer between your computer and network traffic.
When an application attempts to communicate over a network, Windows Firewall can determine whether that communication matches an existing rule.
Rules can be based on factors such as:
- Application
- Port
- Protocol
- IP address
- Network profile
- Direction of traffic
Windows supports different network profiles, including:
- Domain
- Private
- Public
Microsoft explains that public networks generally receive stricter security treatment because other devices on those networks may not be trusted. A home network is commonly configured as Private, while a coffee-shop Wi-Fi network is an example of a Public network. (Microsoft Support)
This distinction matters when creating firewall rules. A rule that is appropriate for a trusted private network may not be appropriate for every public network.
How Do I Find My Windows Firewall?
The easiest way to find Windows Firewall in Windows 10 or Windows 11 is through Windows Security.
Open:
Start → Windows Security → Firewall & network protection
Microsoft identifies Firewall & network protection as the Windows Security section used to view and manage Windows Firewall status. (Microsoft Support)
You can also search for Windows Security from the Start menu.
Another method is to open the traditional Control Panel firewall interface.
Press:
Windows + R
Then enter:
firewall.cplPress Enter.
Microsoft documents firewall.cpl as the Control Panel applet for basic Windows Firewall configuration. (Microsoft Learn)
For advanced configuration, press Windows + R, enter:
wf.mscand press Enter.
This opens Windows Defender Firewall with Advanced Security, which provides detailed inbound and outbound rule management. (Microsoft Learn)
How Do I Check If Windows Firewall Is Enabled or Disabled?
There are several ways to check the current firewall status.
The easiest method is:
Start → Windows Security → Firewall & network protection
Windows Security displays the firewall status for the available network profiles. Microsoft provides this interface specifically for viewing and managing firewall status. (Microsoft Support)
You can also use the classic Control Panel:
Control Panel → System and Security → Windows Defender Firewall
For advanced users, wf.msc provides access to Windows Defender Firewall with Advanced Security.
Another option is the command line. Microsoft documents the netsh advfirewall command for managing Windows Firewall configuration. (Microsoft Learn)
For example, an administrator can query firewall state with:
netsh advfirewall show allprofilesThis can provide information about firewall settings across the available network profiles.
Should I Turn On or Off the Windows Firewall?
For normal Windows use, Microsoft recommends keeping Windows Firewall enabled.
Microsoft states that turning off Windows Firewall can make a device more vulnerable to unauthorized access. If an application is being blocked, Microsoft recommends allowing the application through the firewall rather than turning the firewall off entirely. (Microsoft Support)
A firewall is particularly important when a computer connects to networks that are not fully trusted.
Turning the firewall off can remove an important network-filtering layer. This does not mean that the computer instantly becomes compromised, but it does remove protection that would otherwise restrict certain unauthorized connections.
If a particular program does not work, the better approach is usually to identify what communication it requires and create an appropriate exception.
Is It Safe to Turn Windows Firewall Off?
Temporarily disabling Windows Firewall can be appropriate for certain troubleshooting situations, but leaving it disabled unnecessarily increases exposure to unauthorized network access.
Microsoft specifically warns that turning off Windows Firewall could make the device more vulnerable. (Microsoft Support)
If a game, application, server, or development tool is not connecting properly, disabling the entire firewall is generally broader than necessary.
Instead, you can create a rule that permits the required application, port, protocol, or connection.
This allows the firewall to continue protecting other network traffic.
How Do I Stop My Firewall From Blocking an Application?
If Windows Firewall is blocking an application that you trust, you can add it to the allowed-app list.
In Windows Security:
Windows Security → Firewall & network protection → Allow an app through firewall
Then select:
Change settings
You can select an existing application or use Allow another app to specify the application. Microsoft documents this method as a way to allow an application without disabling the entire firewall. (Microsoft Support)
This approach is often preferable to turning the firewall off because the exception can be limited to the specific application.
Before allowing an application, make sure you recognize it and trust its source.
Microsoft specifically advises users not to allow applications they do not recognize to communicate through the firewall. (Microsoft Support)
How Do I Open Port 9999 on Windows?
Port 9999 is not automatically a special Windows port. An application or service may use it for a particular purpose, so you should first confirm which program requires it and whether it uses TCP or UDP.
To create an inbound firewall rule for port 9999:
- Open Windows Security.
- Select Firewall & network protection.
- Select Advanced settings.
- Choose Inbound Rules.
- Select New Rule.
- Select Port.
- Choose TCP or UDP, depending on the application’s requirements.
- Enter
9999as the specific local port. - Select Allow the connection.
- Choose the appropriate network profiles.
- Give the rule a recognizable name.
- Finish the wizard.
Microsoft documents this general procedure for opening a port through Windows Firewall. (Microsoft Support)
Do not open a port simply because a website, application, or random troubleshooting guide mentions it. Microsoft notes that opening a port is more risky than allowing a specific application because an open port can remain available until the rule is closed. (Microsoft Support)
What Is TCP Port 9999?
TCP port 9999 is simply a numbered TCP network port.
A port number identifies a logical communication endpoint on a computer. Port 9999 does not inherently represent one universal Windows service.
Different software can use the same port number for different purposes.
Therefore, if you encounter TCP 9999, you should determine which application or service is requesting it before creating a firewall rule.
For a local development environment, for example, a developer may configure an application to listen on port 9999. A network administration tool could also use a particular port.
The firewall rule should match the actual application and protocol requirements rather than assuming that port 9999 always has one purpose.
How Do I Open Port 7777?
Opening port 7777 follows the same Windows Firewall process.
Go to:
Windows Security → Firewall & network protection → Advanced settings → Inbound Rules → New Rule
Select Port, then specify:
7777Choose TCP or UDP according to the application that needs the connection.
If both protocols are genuinely required, separate rules can be created for TCP and UDP.
The important part is identifying the actual requirement before opening the port.
For example, a game server might use one protocol and port combination while another application uses the same numerical port differently.
Opening an unnecessary port increases the computer’s network exposure, so rules should be limited to what the application actually needs. Microsoft explicitly recommends opening ports only when necessary and closing them when they are no longer needed.
TCP vs UDP When Creating Firewall Rules
One of the most common firewall configuration mistakes is selecting the wrong protocol.
TCP provides connection-oriented communication and is commonly used when applications require reliable delivery.
UDP is connectionless and is often used when low overhead or real-time communication is important.
A firewall rule for TCP does not automatically mean that UDP traffic on the same port is permitted.
For example, a rule for:
TCP 7777is different from:
UDP 7777If software documentation says that it requires UDP 7777, creating only a TCP rule will not provide the required access.
Always use the protocol specified by the application.
Will a Firewall Stop Hackers?
A firewall can reduce certain network security risks, but it is not a complete security solution.
Windows Firewall filters network traffic and can block unauthorized connections based on configured criteria. Microsoft describes Windows Firewall as a component that helps protect devices by filtering network traffic and restricting unauthorized access. (Microsoft Support)
However, a firewall does not replace:
- Antivirus protection
- Security updates
- Strong passwords
- Multi-factor authentication
- Secure application configuration
- Safe browsing habits
- Backup strategies
For example, a firewall cannot automatically make a malicious application safe if a user intentionally installs and runs it.
Windows Security combines several security features, including Microsoft Defender Antivirus, Windows Firewall, Smart App Control, and other protections. (Microsoft Support)
A firewall should therefore be considered one security layer rather than a complete defense by itself.
Is Windows Firewall Good?
Windows Firewall is an important built-in Windows security component that provides network traffic filtering without requiring users to install a separate firewall for basic protection.
Microsoft states that Windows Firewall is built into Windows and is enabled by default. (Microsoft Support)
It supports application rules, port rules, network profiles, inbound and outbound filtering, and advanced configuration.
The advanced firewall interface also provides features for connection-security rules and monitoring logs. (Microsoft Support)
For most everyday Windows users, the built-in firewall provides the fundamental functionality needed to control network access.
Advanced users may want additional management tools because Windows Firewall has a large number of configuration options that can be difficult to navigate manually.
Is It Good to Turn On the Firewall?
Keeping the firewall enabled is part of normal Windows security configuration.
Windows Firewall is designed to filter network traffic and block unauthorized access according to its rules. Microsoft recommends keeping it enabled and suggests allowing individual applications when necessary rather than disabling the firewall completely. (Microsoft Support)
The benefit is particularly relevant on public or untrusted networks.
When connected to a public Wi-Fi network, your computer may be exposed to other devices on that network. Windows applies stricter security considerations to public networks compared with private networks. (Microsoft Support)
For that reason, users should avoid disabling the firewall simply to make an application work.
What Happens If the Firewall Is Off?
When Windows Firewall is turned off, the operating system loses that firewall filtering layer for the affected network profile.
This can increase exposure to unauthorized network connections.
Microsoft explicitly warns that turning off Windows Firewall can make the device more vulnerable to unauthorized access. (Microsoft Support)
This does not mean every computer with its firewall temporarily disabled will immediately be attacked. Other security mechanisms may still be active.
However, disabling the firewall removes a protective control that would otherwise evaluate network connections.
If an application requires a connection that the firewall is blocking, creating a specific rule is generally more controlled than turning off the entire firewall.
How to Close an Open Windows Firewall Port
Closing an unnecessary port is just as important as opening one.
Open:
Windows Security → Firewall & network protection → Advanced settings
Then select:
Inbound Rules
Find the rule associated with the port.
You can right-click it and choose:
Disable Rule
Microsoft specifically documents disabling an existing rule as the method for closing a port that was previously opened. (Microsoft Support)
If you no longer need the application or service, removing the associated rule can also help keep the firewall configuration clean.
Regularly reviewing old rules is useful on computers where many applications have been installed over time.
Windows Firewall Control Panel
The classic Windows Firewall Control Panel interface is still available on supported Windows versions.
One of the quickest ways to open it is:
Windows + R → firewall.cpl → Enter
Microsoft documents this command as the Control Panel applet for Windows Firewall. (Microsoft Learn)
The Control Panel interface provides basic firewall settings, while more advanced configuration is available through Windows Defender Firewall with Advanced Security.
For users who need to create specific inbound and outbound rules, wf.msc is generally the more appropriate built-in interface.
Windows Firewall Advanced Security
Windows Defender Firewall with Advanced Security provides considerably more control than the basic Windows Security interface.
It allows administrators and advanced users to manage:
- Inbound rules
- Outbound rules
- Connection security rules
- Monitoring
- IP-based restrictions
- Port restrictions
- Application-based rules
- Network profiles
Microsoft documents wf.msc as the command used to open Windows Defender Firewall with Advanced Security. (Microsoft Learn)
This interface is especially useful for developers, system administrators, gamers running servers, and users troubleshooting network applications.
However, changing advanced rules incorrectly can cause applications to stop working or expose services unnecessarily. Microsoft also warns that incorrect firewall configuration can make systems more vulnerable. (Microsoft Support)
Windows Firewall Control and Third-Party Management Tools
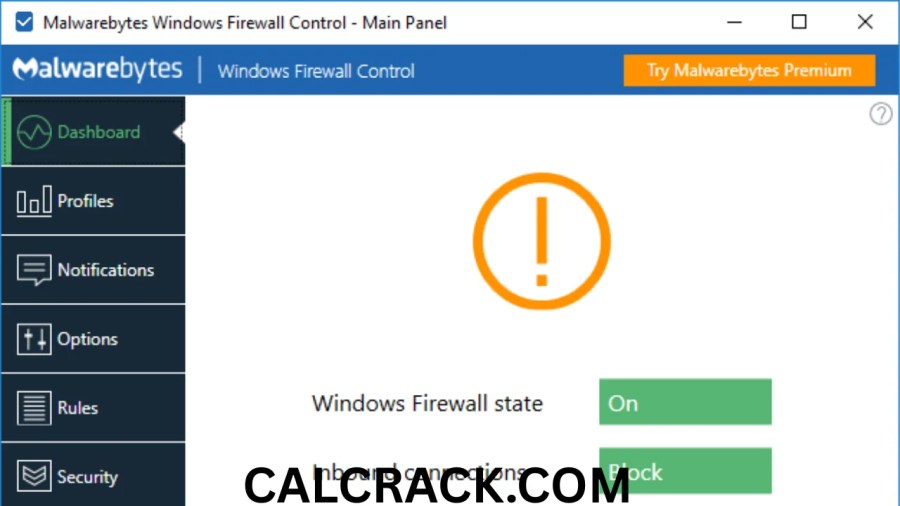
Some users search specifically for Windows Firewall Control (WFC) because they want a more convenient interface for managing Windows Firewall.
Third-party firewall management utilities can provide easier rule creation, notifications, filtering, and monitoring than the default Windows interface.
However, these utilities generally work with the Windows filtering and firewall infrastructure rather than replacing the basic concept of network filtering.
Before installing any third-party firewall-control software, download it from a trusted source and understand what changes it makes to Windows Firewall.
If the goal is simply to allow one application or open one port, Windows’ own firewall tools may already provide everything required.
Windows Firewall Control and Malwarebytes
Another common search query is Windows Firewall Control Malwarebytes.
Malwarebytes and Windows Firewall serve different security functions.
A firewall primarily controls network traffic, while antimalware software focuses on detecting and responding to malicious software.
Microsoft describes Windows Security as a broader security environment containing Windows Firewall alongside Microsoft Defender Antivirus and other security features. (Microsoft Support)
Installing additional security software does not mean the firewall should automatically be disabled. The correct configuration depends on the specific products installed and how they integrate with Windows.
Users should also avoid running conflicting security configurations without understanding which product is responsible for firewall filtering.
How to Allow an Application Instead of Opening a Port
For many situations, allowing an application is more targeted than opening a port.
Microsoft explicitly states that adding an application to the allowed list is generally less risky than opening a port because the application exception can open the required ports when needed, while a manually opened port can remain open until the user closes it. (Microsoft Support)
To allow an application:
Windows Security → Firewall & network protection → Allow an app through firewall
Then select Change settings.
Choose the application and select the appropriate network profiles.
This method can be useful for:
- Games
- Browsers
- Development tools
- Media servers
- File-sharing applications
- Communication software
Only allow applications that you recognize and trust.
How Windows Firewall Handles Public and Private Networks
Windows Firewall uses different network profiles because not every network has the same level of trust.
A Private network is normally intended for trusted environments such as a home network.
A Public network is intended for environments where other connected devices may not be trusted.
Microsoft recommends stricter security controls for public networks because other devices on those networks may potentially communicate with your computer. (Microsoft Support)
When creating a firewall rule, therefore, pay attention to which profiles are selected.
A rule that works on a Private network does not necessarily need to be enabled on Public networks.
Restricting a rule to the profile where it is genuinely required can reduce unnecessary exposure.
Windows Firewall Rules for Gaming
Gamers sometimes need to configure Windows Firewall because multiplayer games, dedicated servers, or communication services may require particular inbound or outbound connections.
If a game specifically documents a port requirement, users can create a corresponding firewall rule rather than disabling Windows Firewall.
For example, if a game server requires port 7777, the user should confirm:
- Whether it requires TCP or UDP
- Whether the rule is inbound or outbound
- Which network profile is needed
- Whether the game executable itself can be allowed instead
- Whether the router also requires port forwarding
Windows Firewall and router port forwarding are different things.
Opening a port in Windows Firewall does not automatically make that port accessible from the public internet. A router or NAT device may still block inbound traffic.
Windows Firewall and Port Forwarding Are Not the Same
This distinction is important when configuring servers.
A Windows Firewall rule controls whether Windows allows matching traffic to reach or leave the computer.
Router port forwarding controls whether incoming traffic from outside the local network is forwarded to a specific device.
For an internet-accessible service, both layers may need appropriate configuration.
However, opening ports to the internet should be done carefully because Microsoft notes that opening a port can increase security risk and create opportunities for unauthorized access. (Microsoft Support)
Only expose services that are genuinely required, and close the configuration when the service is no longer needed.
Best Practices for Windows Firewall Control
A few simple practices can make firewall management safer and easier.
Keep the Firewall Enabled
For normal Windows use, keep Microsoft Defender Firewall enabled.
Allow Applications When Practical
If an application can be safely added to the allowed-app list, this may be preferable to opening a permanent port. (Microsoft Support)
Open Only Required Ports
Do not open random ports simply because they appear in a troubleshooting guide.
Choose the Correct Protocol
Check whether the application requires TCP, UDP, or both.
Use the Correct Network Profile
Avoid enabling a rule on Public networks when the application only needs it on a trusted Private network.
Remove Old Rules
When software is uninstalled or a temporary server is shut down, review and remove unnecessary firewall rules.
Do Not Allow Unknown Applications
Microsoft specifically recommends avoiding firewall permissions for applications you do not recognize. (Microsoft Support)
Final Thoughts on Windows Firewall Control
Windows Firewall Control provides users with several ways to manage network protection on Windows 10 and Windows 11. The built-in Microsoft Defender Firewall filters network traffic and can control connections according to applications, ports, IP addresses, and other criteria. (Microsoft Support)
For everyday users, the Firewall & network protection section in Windows Security is usually enough to check firewall status and manage basic settings. For advanced configuration, firewall.cpl opens the classic Control Panel interface, while wf.msc opens Windows Defender Firewall with Advanced Security. (Microsoft Learn)
Ports such as 9999 and 7777 can be opened through an inbound firewall rule when a legitimate application or service requires them. The correct TCP or UDP protocol should be confirmed before creating the rule, and unnecessary ports should be closed when they are no longer needed.
The most important principle is to avoid disabling the entire firewall simply because one application is blocked. Microsoft recommends using an application exception or a specific port rule when appropriate because these approaches can provide more targeted access than turning off Windows Firewall altogether. (Microsoft Support)
With sensible rules, appropriate network profiles, regular updates, and other security protections such as Microsoft Defender Antivirus, Windows Firewall remains an important part of the Windows security system.
Download Now
Windows Firewall Control
File Details:
- File Size: 2.7 MB
- System Type: Not specified
- Setup Type: Not specified
Download Options: